Cybersecurity • Detection Engineering • Cloud Security

Favour Usunobun

Cybersecurity Engineer · Detection Engineering · Security Operations · DevSecOps

I build practical security systems across detection engineering, security monitoring, cloud security, and DevSecOps, with hands-on experience across AWS, SIEM, security automation, and infrastructure security.

Security engineering with a detection-first focus.

My work focuses on turning security telemetry into actionable detections, improving security visibility, assessing cloud environments, and integrating security controls into infrastructure and development workflows.

Detection Engineering

Wazuh SIEM, log-source onboarding, custom decoders, MITRE ATT&CK-mapped detection rules, alert triage, event correlation, and validation.

Cloud & DevSecOps

AWS security, IAM and least privilege, CloudTrail, Terraform, CI/CD security, OPA/Policy-as-Code, SBOM, SAST/DAST, and infrastructure hardening.

Projects

Practical security work with technical evidence, implementation details, and supporting documentation.

Detection Engineering · Solo Project

SecOpsAI

Problem: Improve automated analysis of security events using ML-based detection.

My role: Built the AI-driven threat detection system, including the detection pipeline, supporting application, monitoring, and deployment components.

Evidence: XGBoost classifier achieved 0.9931 F1 score with approximately 26 ms API latency.
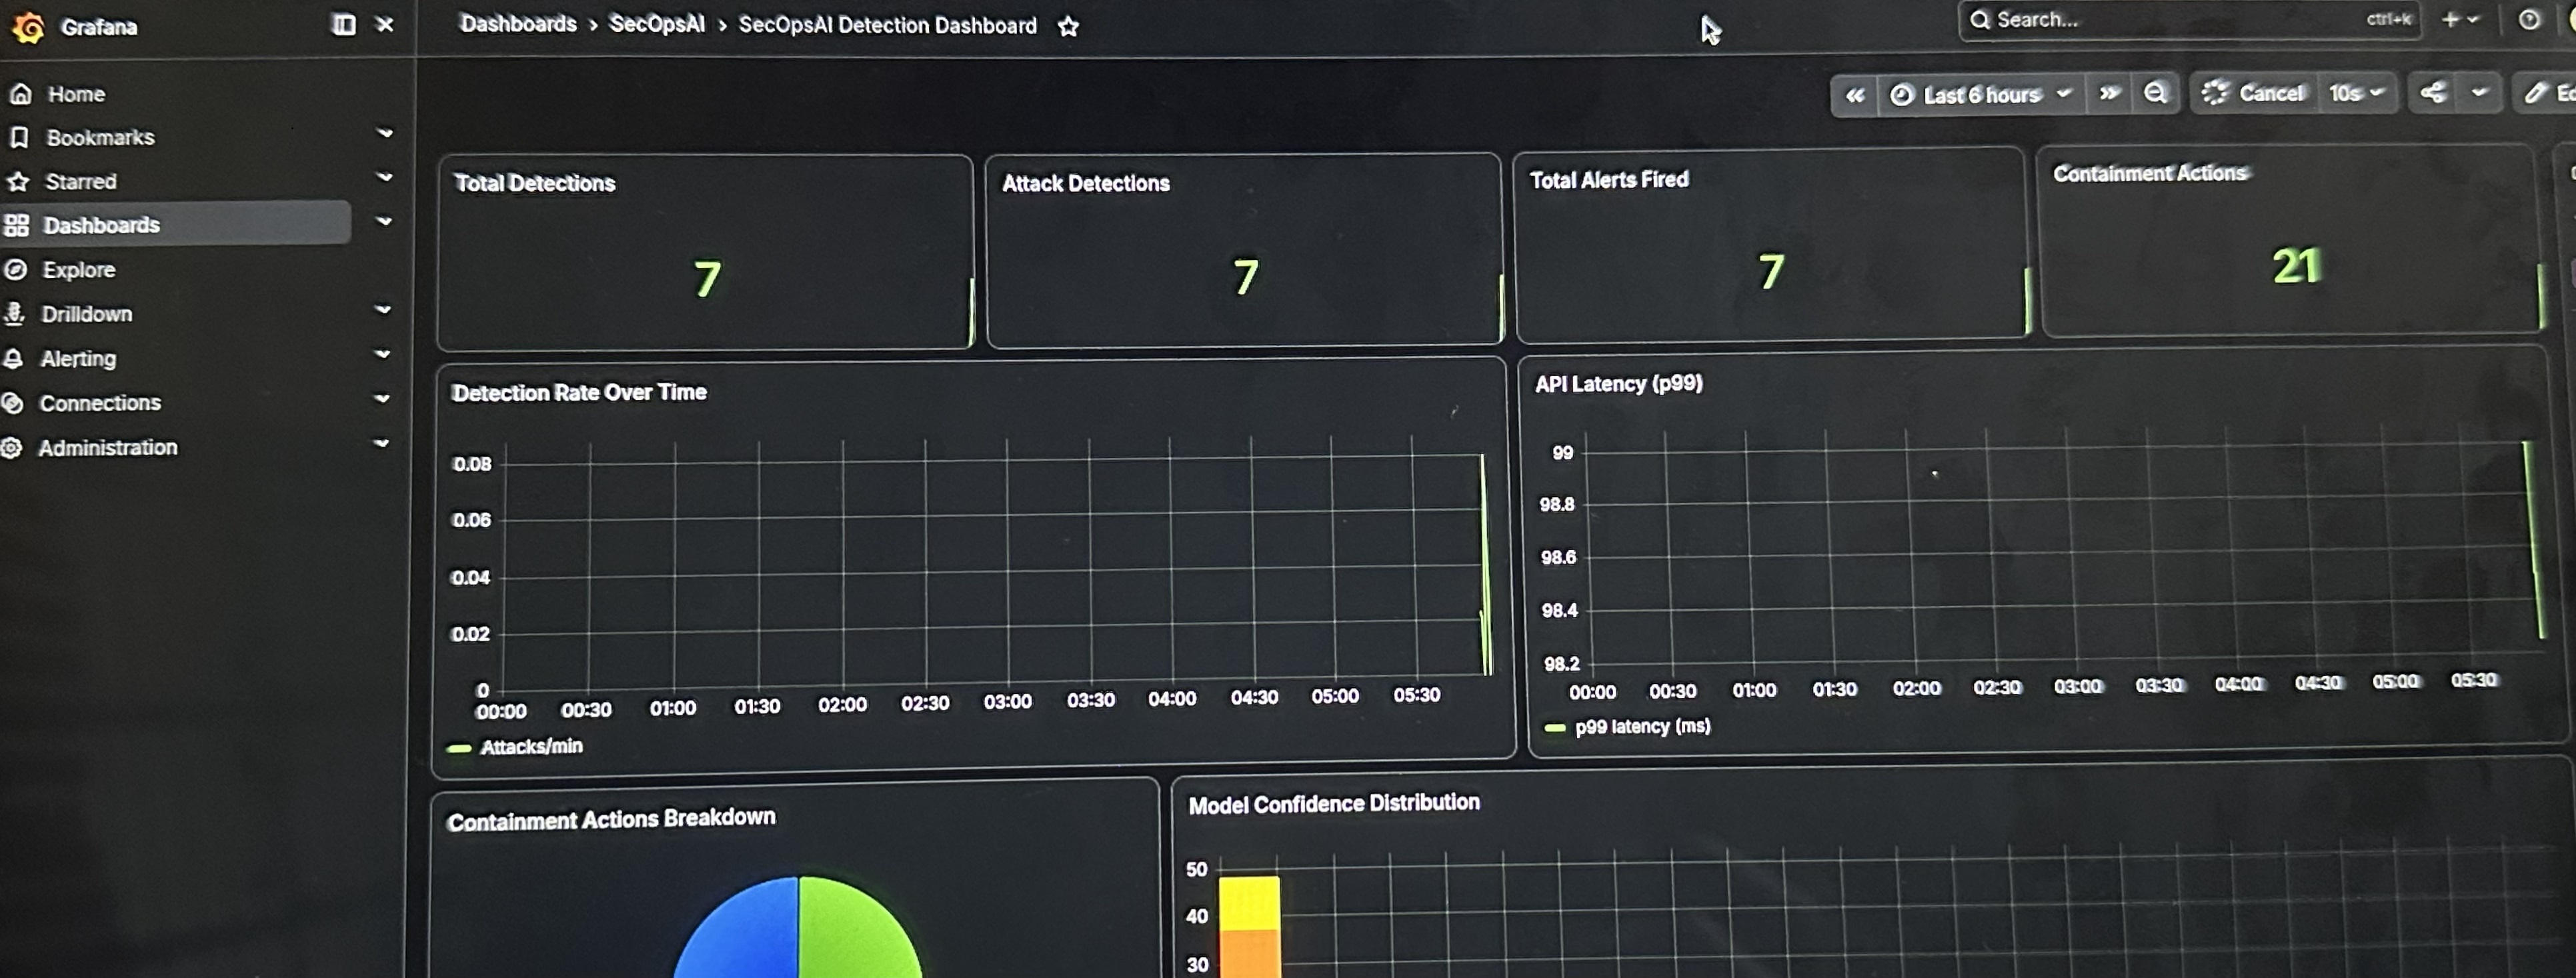
SecOpsAI Grafana monitoring dashboard showing security detection metrics
Detection Engineering XGBoost Python FastAPI Docker Prometheus Grafana
Cloud Security · Infrastructure

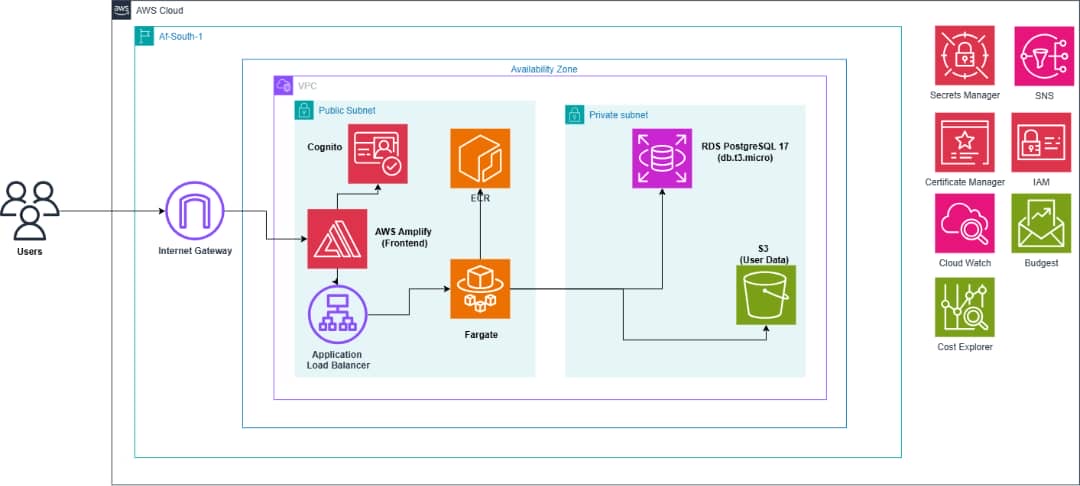
TradeCore

Problem: Design a secure, repeatable AWS environment for a multi-service application.

My role: Worked across the Terraform architecture covering networking, ECS, ALB, RDS, Secrets Manager, and Amplify.

Solution: Modular infrastructure design with secure service connectivity, HTTPS, secrets management, policy enforcement, and GitHub Actions OIDC.

TradeCore AWS architecture diagram
AWS Terraform ECS ALB RDS OPA CI/CD
SIEM · Detection Engineering · Team Project

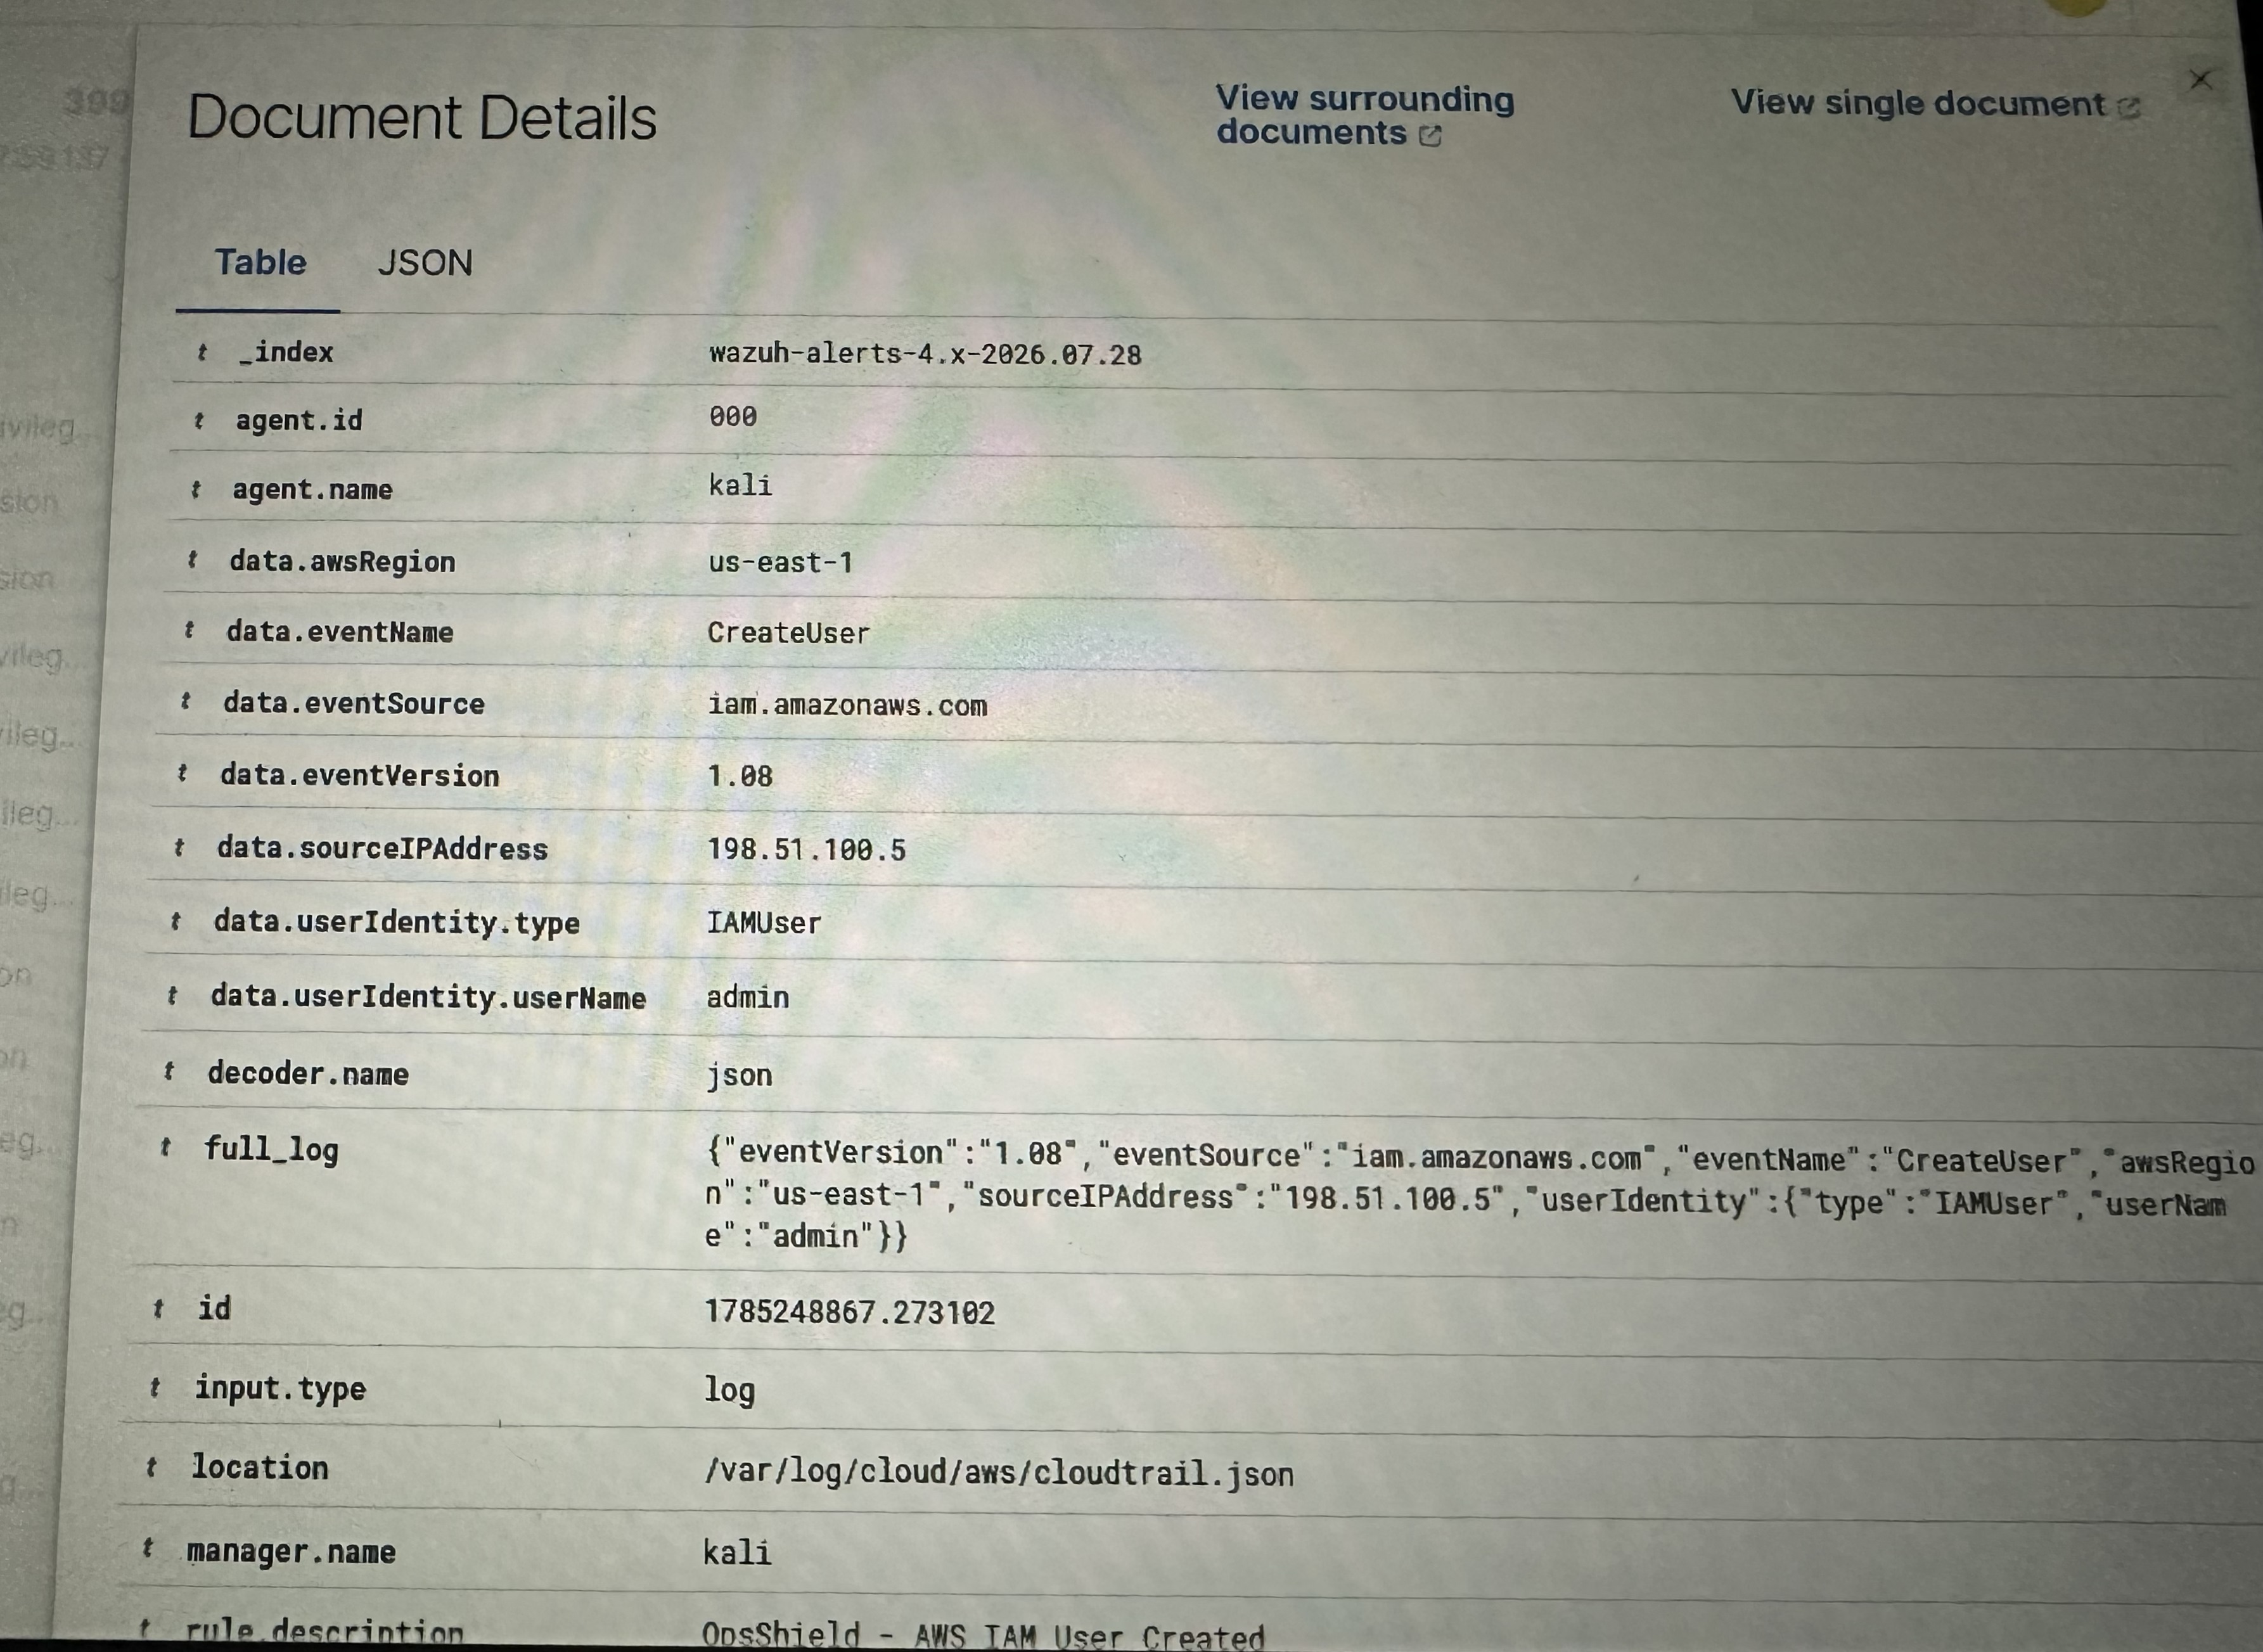
OpsShield

Problem: Centralize cloud and development telemetry for security monitoring and detection.

My role: Owned the monitoring and detection engineering workstream, including Wazuh integration, log analysis, custom decoders, detection rules, event correlation, testing, and validation.

Solution: Centralized Wazuh monitoring across AWS and development telemetry with detection logic mapped to relevant attack techniques.

OpsShield Wazuh dashboard event log showing security monitoring activity
Wazuh AWS CloudTrail Detection Engineering SIEM
SOC · Security Monitoring

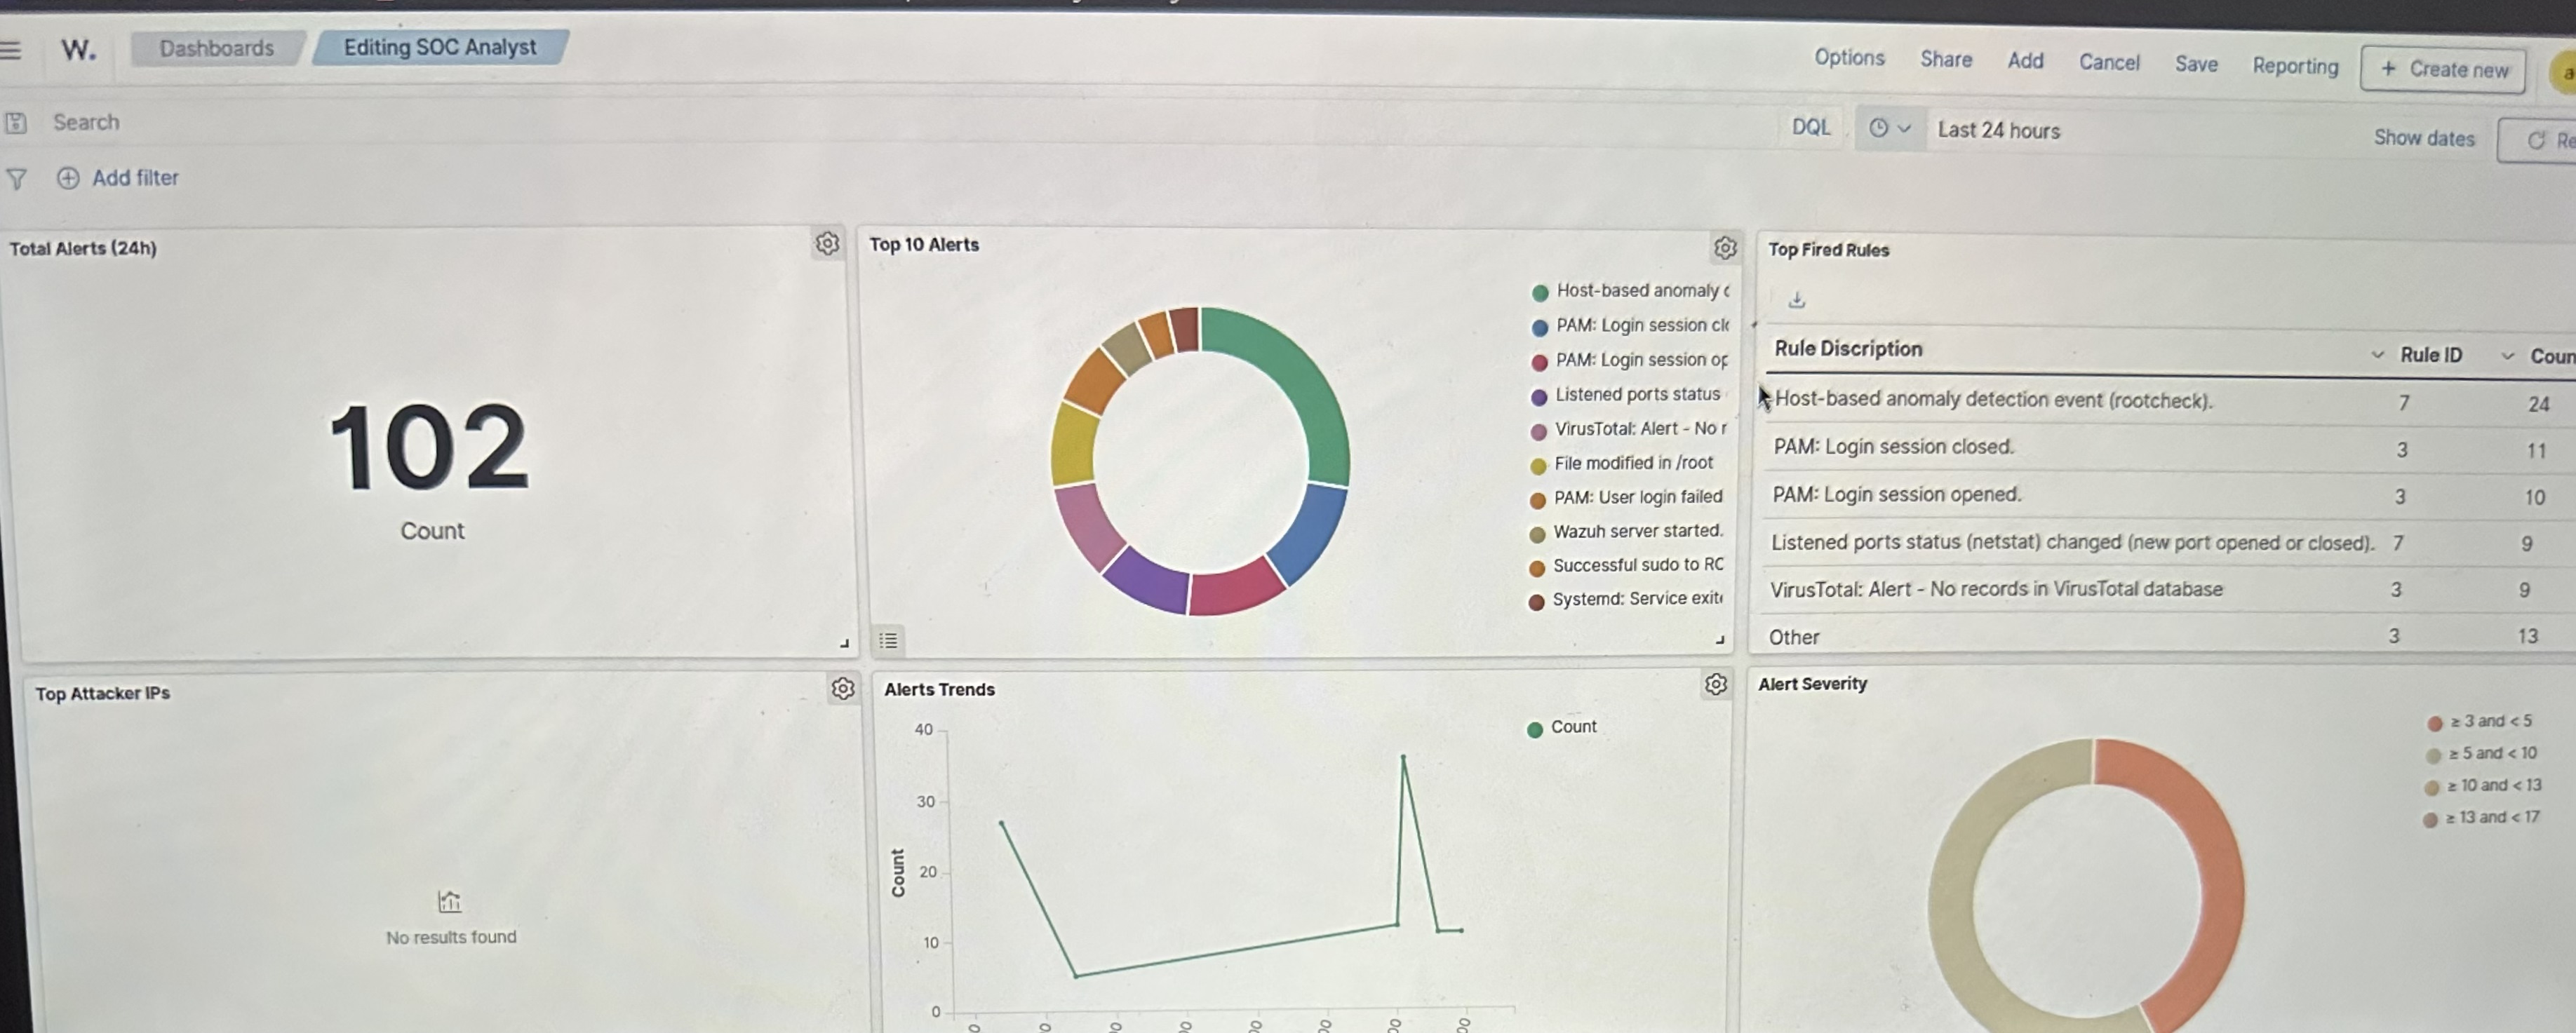
FireOps Systems

Problem: Establish centralized visibility across endpoints, network activity, and cloud infrastructure.

My role: Worked across Wazuh, Suricata, FIM, detection scenarios, AWS CloudTrail integration, dashboards, and SOC investigation workflows.

Validation: Tested brute-force, network reconnaissance, privilege-change, and file-modification scenarios using resulting alerts and investigation workflows.

FireOps Systems SOC dashboard showing centralized security monitoring
Wazuh Suricata AWS CloudTrail FIM SOC
AWS · Security Assessment · Vulnerability Management

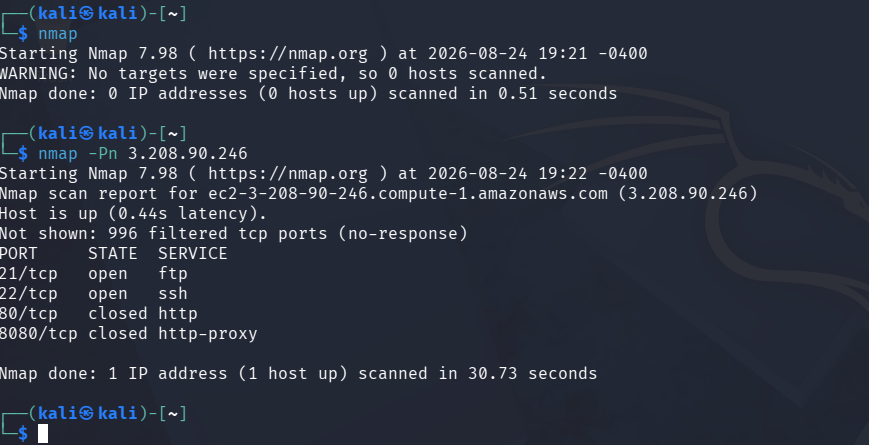
AWS Cloud Security Assessment

Problem: Assess AWS security weaknesses, determine risk, remediate findings, and validate the results.

My role: Conducted the assessment, documented findings and risk ratings, planned remediation, and performed post-remediation validation.

Key findings: EC2 exposure, public RDS, missing MFA, excessive IAM privileges, and disabled S3 public-access controls.

AWS Security Assessment Nmap scan evidence
AWS Security Assessment IAM EC2 RDS S3 Vulnerability Management

Professional Experience

Handi HQ

Security Engineering · Detection Engineering · DevSecOps
  • Security monitoring and detection engineering using Wazuh.
  • Security automation and SOAR workflows with Shuffle.
  • AWS log integration and cloud security monitoring.
  • CI/CD security, OPA/Policy-as-Code, and SBOM troubleshooting.
  • SAST/DAST, Linux/VPS security, Nginx, and SSL/TLS configuration.
  • Security resilience and failover architecture research.
Private company infrastructure — technical details and source code are not publicly available.

Expadox Limited

Cybersecurity & Cloud Engineering Intern / Mentee
  • Contributed to cybersecurity operations and infrastructure-security initiatives under mentorship from experienced security engineers.
  • Hands-on exposure to cloud infrastructure and architecture, including AWS and cloud security concepts.

What I work across

Detection Engineering

Detection logic, decoders, ATT&CK mapping, alert validation, and security telemetry.

Security Operations

SIEM monitoring, event correlation, investigation workflows, and SOC visibility.

Cloud Security

AWS IAM, CloudTrail, network controls, security assessments, and remediation.

DevSecOps

Terraform, CI/CD security, OPA, SBOM, SAST/DAST, secrets management, and secure infrastructure.

Education and training

Education

  • BSc in Science Laboratory Technology (Biochemistry), Ekiti State University, 2024

Training and mentorship

  • Expadox Limited: Cybersecurity and Cloud Engineering Internship / Mentorship
  • TS Academy: Cybersecurity Program
  • SheCodeAfrica: Cybersecurity Learning
  • Tech4Dev: Cybersecurity Training
  • Blooming Hearts Foundation: Cloud Computing (AWS)

Let's connect.

Open to cybersecurity, detection engineering, security operations, cloud security, and DevSecOps opportunities.